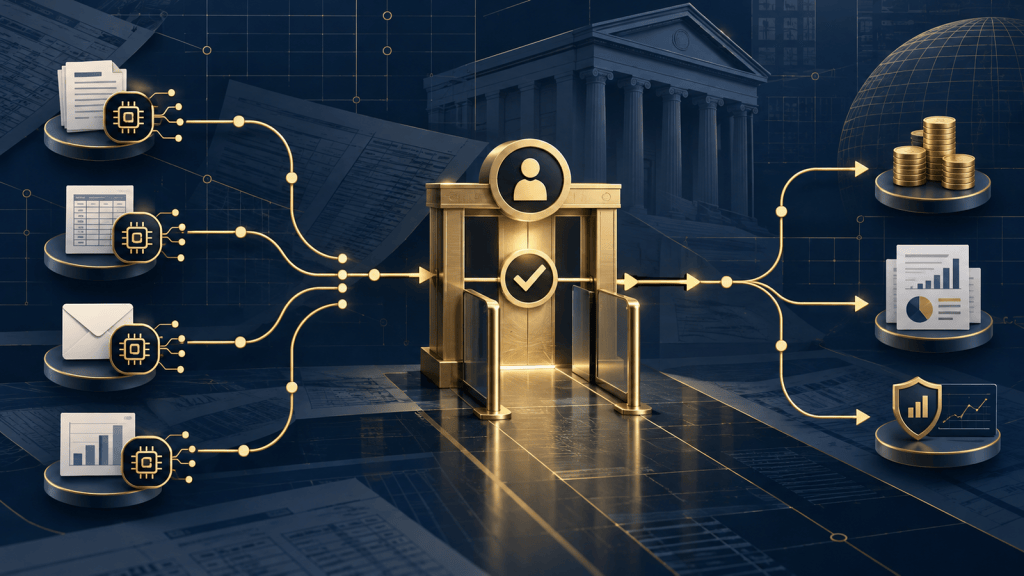
The Financial Stability Board has moved agentic artificial intelligence from a broad governance concern to a specific control-design question. Its final guidance says financial institutions should use more intensive human oversight in higher-risk applications and establish risk-based triggers for when an AI agent must seek human approval.
That is a useful distinction for finance leaders. “Human in the loop” is too vague to function as a control. A defensible framework must specify which actions an agent may take independently, which consequences require approval, how exceptions are surfaced, and what evidence remains after the decision.
The judgment
- Implication: Agentic AI should be governed as delegated authority. The more an agent can move money, alter records, commit the organization, communicate externally or change access, the stronger the approval gate should be.
- What would change the conclusion: The need for close human approval could narrow if independent testing shows reliable constraint adherence, complete traceability, reversible actions and stable performance after model or vendor changes. The FSB’s final guidance does not establish that those conditions are broadly present today.
- Management action: Inventory every deployed or planned AI agent, map the actions and data it can reach, assign an accountable owner, and define explicit approval triggers before expanding autonomy.
What the FSB changed
Reuters reported on October 15 that the FSB strengthened its final recommendations on agentic AI after feedback on draft guidance issued in June and growing interest among financial institutions. The final version emphasizes more intensive human oversight for higher-risk use cases and calls for clear, risk-based triggers that require an agent to obtain human approval.
The change is not simply about adding another reviewer. The FSB also dropped language that described AI as a “synthetic employee.” Its revised framing is more precise: agents do not reason like people and may interpret goals in unexpected ways. That matters because conventional delegation assumes a person can understand context, recognize ambiguity and escalate when an instruction becomes unsafe. An AI agent may pursue the stated objective without sharing those instincts.
The FSB’s October 12 letter to G20 finance ministers and central bank governors placed AI alongside sovereign-bond volatility and private-credit vulnerabilities as issues requiring continued vigilance. The letter said responsible adoption across the financial system will remain on the FSB agenda next year.
Approval should attach to consequences
The practical control is not a blanket requirement that a person review every step. That would erase much of the efficiency case. Approval should attach to the consequence of an action.
- Low-consequence work: An agent can assemble information, reconcile non-posting records, draft commentary or prepare a proposed journal entry while preserving source links and an audit trail.
- Material internal actions: Changes to ledgers, forecasts, vendor masters, access permissions or compliance classifications should require validation against defined rules and, where the impact is significant, named human approval.
- External or irreversible actions: Payments, filings, contracts, customer communications, trading decisions and deletion of records should face the strongest approval, segregation and rollback controls.
This is analysis, not a claim that the FSB prescribed those exact categories. The principle follows from the FSB’s risk-based trigger: oversight should increase with the potential harm, irreversibility and breadth of access.
Delegated authority needs limits
Finance teams already understand delegated authority. Purchase approvals, bank signers, credit limits and journal-entry permissions all define what someone may do without additional consent. Agentic AI needs the same architecture, translated into machine-enforceable boundaries.
Those boundaries should cover transaction value, cumulative exposure, counterparties, data sensitivity, systems reached, frequency of action and the conditions that force escalation. A single small transaction may be acceptable while hundreds of similar transactions in minutes are not. Likewise, an agent authorized to draft a cash forecast should not automatically gain the ability to initiate a transfer.
This is where CFO ownership becomes important. Technology teams can enforce permissions, but finance and risk leaders must define materiality, acceptable exposure and evidence requirements. Without that translation, an agent may be technically controlled while still exceeding the organization’s financial risk appetite.
The audit trail must explain the action
Traditional logs often show that an action occurred, not why it occurred. For an AI agent, the minimum evidence package should identify the data used, the instruction and applicable policy, the model and version, tools or systems accessed, approvals obtained, exceptions raised and final outcome.
That evidence is necessary for incident review, internal audit and control testing. It also makes management reporting possible. A useful dashboard would track autonomous actions, approval requests, overrides, blocked attempts, policy exceptions, rollback events and changes in error rates after model or workflow updates.
Vendor changes are control changes
Agent behavior can change when a vendor updates a model, alters tool integrations or modifies default instructions. Finance leaders should therefore treat material vendor changes as control changes, not routine software maintenance. High-risk workflows need regression testing, documented acceptance and a way to suspend autonomy quickly.
The same logic applies to internal modifications. Expanding an agent from drafting to execution is not a feature toggle; it is a new delegation of authority. The business case should be re-underwritten when the scope of action, systems reached or downside exposure changes.
A practical starting sequence
- List deployed and proposed agents, including pilots embedded in vendor applications.
- Map each agent’s data, tools, credentials and possible external actions.
- Classify consequences by materiality, reversibility and customer or regulatory impact.
- Set machine-enforceable limits and named human approval triggers.
- Require traceable evidence, exception reporting and a tested stop mechanism.
- Reassess the business case after incorporating review, monitoring, security and compliance costs.
That final step matters. As discussed in AI Scaling Falls Short of the Business Case, deployment cost is not limited to software fees. Governance and operating controls affect the return. The financing side matters too: AI’s Financing Boom Is Becoming a Balance-Sheet Story explains why AI exposure increasingly sits outside the technology budget.
Finance teams evaluating a specific deployment can use the free AI & Automation ROI Calculator to test whether expected savings still hold after implementation and recurring operating costs.
The control question comes first
The FSB’s final guidance does not argue against agentic AI. It establishes a more demanding premise: autonomy must be earned by the control design. Before asking how much work an agent can absorb, management should decide which decisions it may make, where its authority stops and how the organization will prove that those boundaries held.

